When this article was first published in July 2022, it covered proposals in the Data Protection and Digital Information Bill. That Bill did not become law; it fell when Parliament was dissolved ahead of the July 2024 general election. Several of its marketing proposals were carried into the Data (Use and Access) Act 2025 (DUAA), which received Royal Assent on 19 June 2025. The changes to the Privacy and Electronic Communications Regulations (PECR) covered below came into force on 5 February 2026.
This article was updated in October 2026 to describe the law as it now stands. It covers three changes that matter most to marketers: the charitable purpose soft opt-in, higher PECR fines, and new exceptions to cookie consent.
Charities can now use the soft opt-in
The soft opt-in allows an organisation to send marketing emails and texts to existing customers without their explicit consent, as long as the details were collected during a sale or negotiation for a sale, the marketing is about similar products or services, and the person was given a simple way to opt out at the time and in every message.
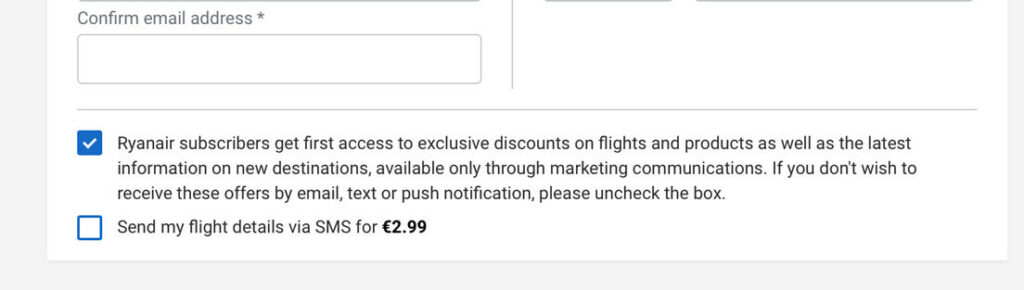
For example, an online shop can tell customers at checkout that it will send them offers on similar products unless they untick a box, and include an unsubscribe link in every email.
Until 2026, charities could not use the soft opt-in because they do not usually sell products or services. Since 5 February 2026, a new charitable purpose soft opt-in allows charities to send marketing emails and texts without consent where:
- the sole purpose of the marketing is to further one or more of the charity’s charitable purposes
- the charity collected the person’s contact details directly, when the person expressed an interest in, or offered or gave support for, those purposes
- the person was given a simple way to opt out when their details were collected, and is given one in every message
It cannot be used to promote commercial products, even where the profits go to the charity. The DUAA extension applies to charities only. The ICO has published guidance on the charitable purpose soft opt-in, and our article on when UK marketers can use the soft opt-in covers the general rules.
PECR fines now match UK GDPR
Fines under PECR used to be capped at £500,000. For breaches on or after 5 February 2026, the ICO can fine up to £17.5 million or 4% of global annual turnover, whichever is higher, the same maximum as for the most serious UK GDPR breaches.
This applies to all PECR breaches, including unsolicited marketing calls, emails and texts, and unlawful use of cookies and similar tracking technologies. Organisations should check that their consent records, suppression lists and Telephone Preference Service screening are up to date, so they can show what they did if something goes wrong.
Some cookies no longer need consent
PECR requires consent before storing or accessing information on a user’s device, unless an exception applies. Strictly necessary cookies were already exempt. Since 5 February 2026, three more exceptions apply:
- Statistical (analytics) cookies, used only to collect information about how a website or service is used so that the operator can improve it. The data must be used only by the operator.
- Appearance and functionality cookies, which adapt how a site looks or works to the user’s choices, such as language or accessibility settings.
- Emergency assistance, where a device’s location is identified so that emergency help can be provided.
For analytics and functionality cookies, users must be given clear information about the purpose and a simple, free way to opt out. In practice, most sites will still need a cookie banner or preference centre, both to record opt-outs and to collect consent for cookies that are not exempt.
Advertising and tracking cookies still need consent. So does any cookie used for more than one purpose where one of those purposes is not exempt, such as an analytics tool that also shares data with an advertising platform. Our article on the ICO’s updated cookie rules covers how to check your setup.
UK and EU visitors
These exceptions apply under UK law only. If your website serves visitors in the EU, the ePrivacy rules in each EU country still apply to them, and those generally require consent for analytics cookies. Organisations with EU audiences will need to decide whether to apply different cookie settings by location or to keep the stricter EU approach for everyone.
Did the changes affect EU adequacy?
An earlier version of this article noted the risk that UK reforms could lead the European Commission to withdraw the UK’s adequacy decisions, which allow personal data to flow freely from the EU to the UK. After reviewing the DUAA, the Commission renewed the UK’s adequacy decisions on 19 December 2025, until 27 December 2031.
What marketers should do
- If you work for a charity, review whether the charitable purpose soft opt-in fits your supporter journeys, and update sign-up forms so that the opt-out is offered at the point of collection.
- Audit your cookies and tags. Identify which ones fall within the new exceptions and which still need consent.
- Update your cookie notice and privacy notice to explain any cookies you now set without consent, and how users can opt out.
- Review your electronic marketing compliance in light of the higher fines, including consent records, suppression lists and TPS screening.
Our GDPR and PECR training courses cover these rules for marketing teams.


